# Take control of your Kubernetes clusters
Natively manage your APIs in Kubernetes to seamlessly implement policies for security, identity, traffic management, and more across every cluster[](https://konghq.com/contact-sales)
Natively manage Kong via Kubernetes CRDs to deliver auto-scaling and eliminate the risk of disruptions caused by configuration drift.
Implement security and identity policies directly into your YAML file to ensure consistency across VM and kubernetes workloads.
Automatically generate Kong Declarative or Kong Ingress Controller configurations with directly from OpenAPI spec files anywhere in your CI/CD pipeline.
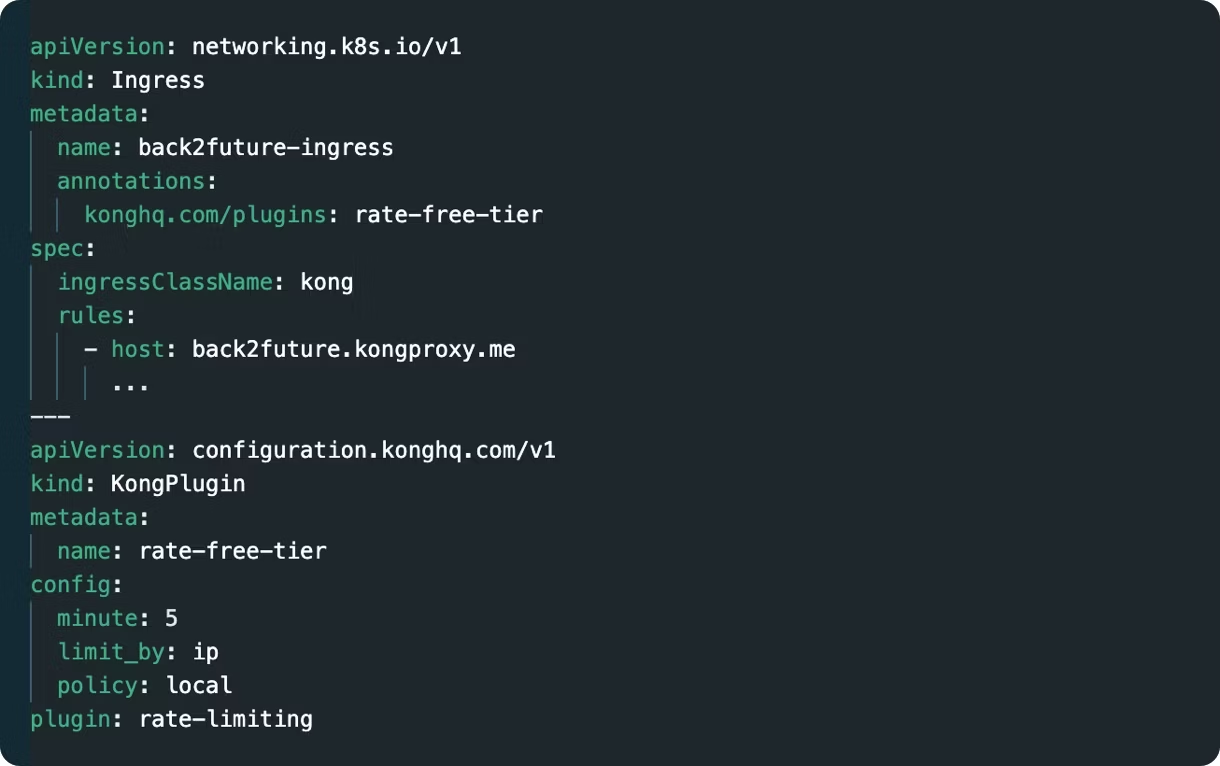
## Kubernetes-native API Management
Configure Kong Gateway the same way as k8s, using kubectl with a declarative API to implement traffic management, transformations, and observability across Kubernetes clusters with zero downtime.
- - Gain global visibility at the ingress
- - Natively manage using CRDs
- - Implement rate-limiting and other traffic policies
- - Declarative configuration for Ingress and API Gateway resources
- - OpenShift, AKS, EKS, GKE and more
## Single Source of Truth for Security
Bridge the gap between legacy and cloud-native by unifying Kubernetes security and identity policies with all your other workloads.
- - Support for Kubernetes, VMs and Baremetal
- - Inject security and identity into YAML files
- - Validate specs to ensure that policies are in place


## Workflows Built for GitOps
Seamlessly integrate with Git providers to minimize friction in pushing configurations for your Kubernetes Ingress and API Gateway through the pipeline.
- - Automatic Spec Generation
- - NAutomated testing on every push